Identity & organisation
Collect people, identities, organisations, engagements and personas with hierarchies and responsibility relationships.
USE CASE
Give several connected systems a shared view of a person’s organisational context.
IDENTITY & ORGANIZATION REGISTRY
A verified foundation for identity and access.
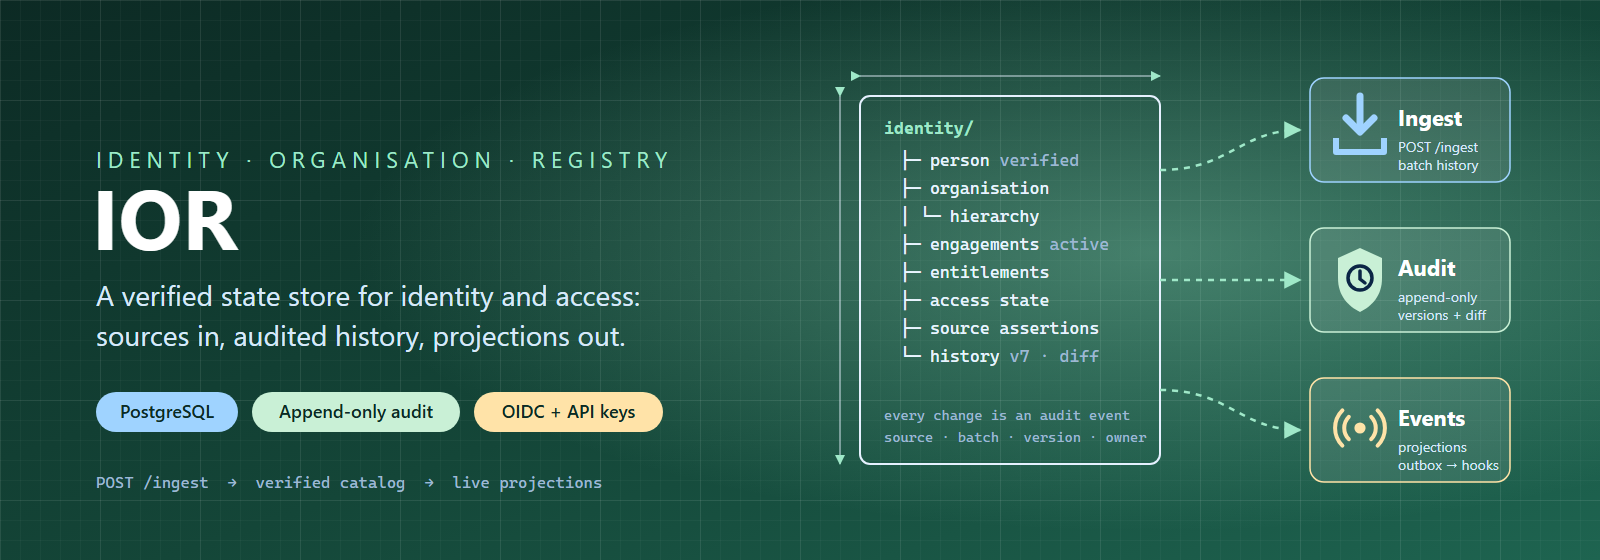
IOR brings identities, organisations and access state into a traceable data platform. Connect source systems, follow every change and deliver current projections to consumers. The registry tracks verified state; requests and approval workflows belong in connected IDM and IGA systems.
PostgreSQL-based registry · OIDC verified locally · Production verification pending
FEATURES & USE CASES
Collect people, identities, organisations, engagements and personas with hierarchies and responsibility relationships.
Give several connected systems a shared view of a person’s organisational context.
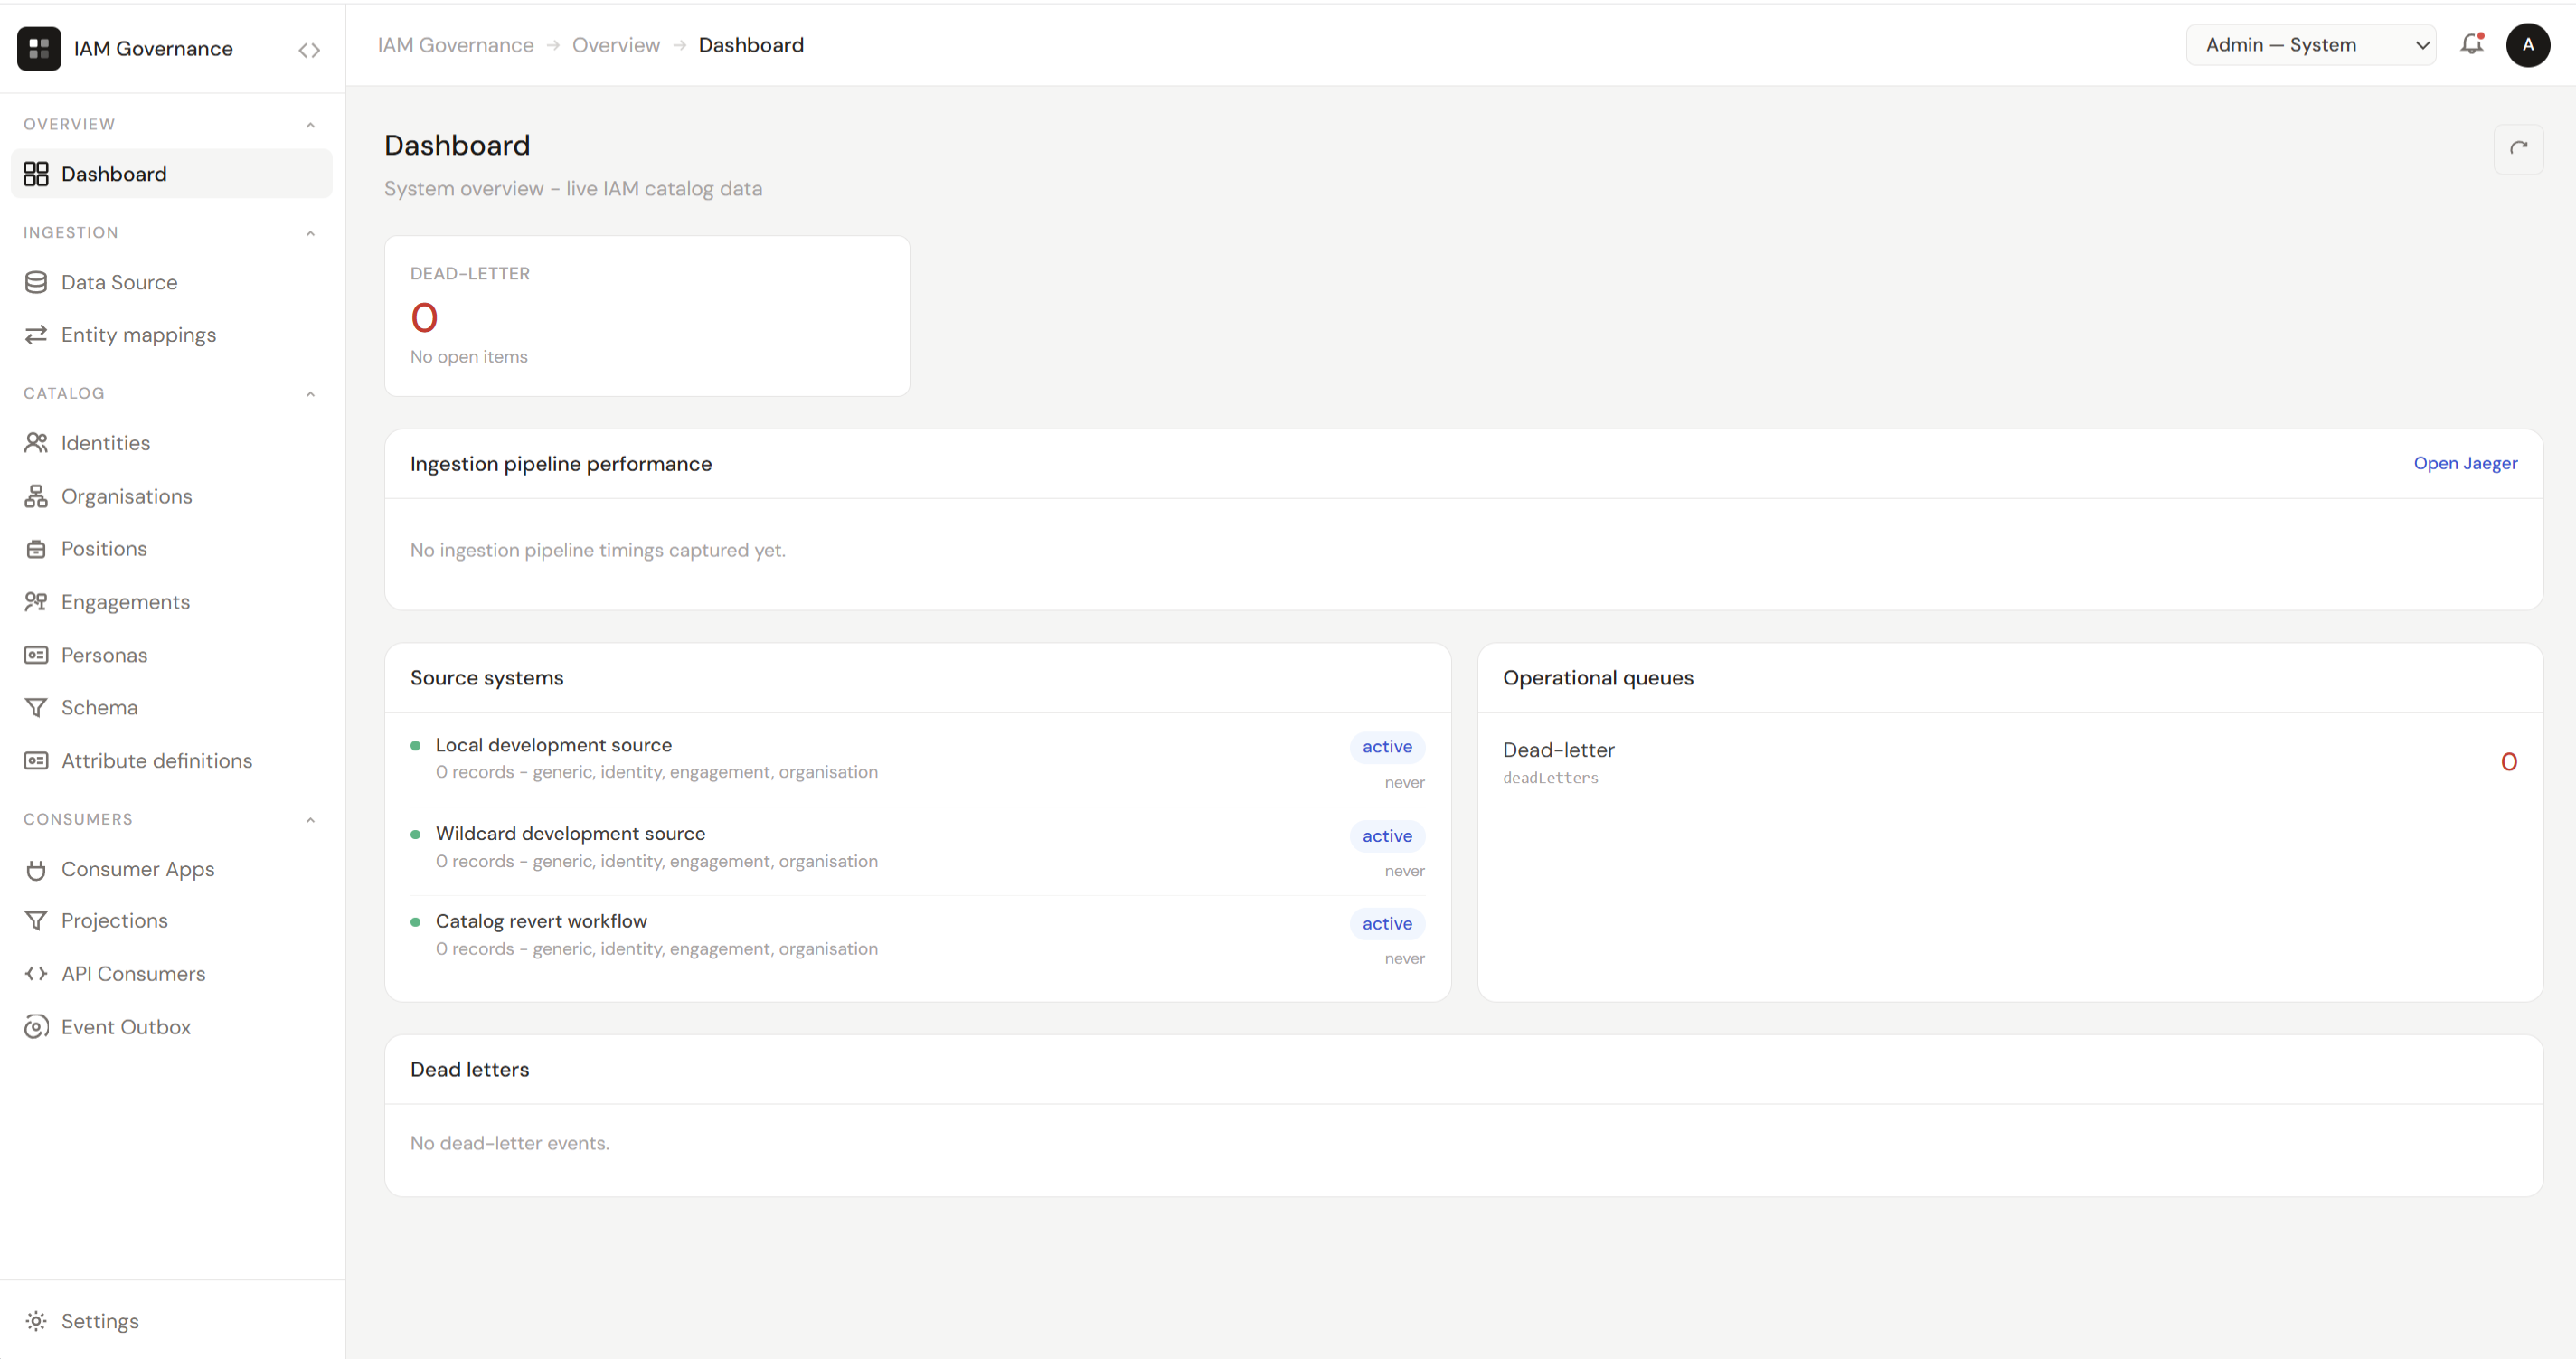
Ingest data through source systems with configured permissions. Review batch history, mapping quality and previews in the dashboard.
Connect an HR source to the registry and check field transformations before regular ingestion.
Source assertions, version history and an append-only audit log make changes traceable. Compare versions to see what changed.
Investigate when an identity gained a new engagement and which source caused the change.
Deliver current identity projections with aliases, data minimisation and cache contracts. An outbox, webhooks and retries support event-driven integrations.
Let a consumer system retrieve only the identity fields it needs.
Manage ingested access assignments, implementation work and reconciliation observations with context for accounts and service accounts.
Compare expected access with observations from a target system.
The dashboard uses OIDC with PKCE and resolved permissions. Machine clients use scoped API keys or tokens, with specific controls for personal data.
Give an operator the right working view and an integration a scoped machine permission.
FROM THE INTERFACE